Connect with us

CyberSecurity

UK Faces a Cyber ‘Perfect Storm’ as Geopolitical Tensions and AI Reshape Threats

Published

on

UK Faces a Cyber ‘Perfect Storm’ as Geopolitical Tensions and AI Reshape Threats

The United Kingdom is navigating what experts call a cyber perfect storm, driven by a convergence of geopolitical strife and rapid technological change. At the CYBERUK 2026 conference in Glasgow, Richard Horne, CEO of the National Cyber Security Centre (NCSC), described the current era as one of “tumultuous uncertainty.” He warned that the combination of artificial intelligence advances and international tensions is creating an unprecedented threat landscape for businesses and individuals alike.

According to the NCSC, the number of nationally significant cyber incidents has remained relatively steady, but the nature of these attacks is evolving. While ransomware remains the most common threat to most organizations, the most dangerous attacks come from nation-state actors. This cyber perfect storm demands a new approach to security—one that prioritizes resilience over simple prevention.

Nation-State Threats: Russia, China, and Iran

Richard Horne outlined how three major adversaries—Russia, China, and Iran—are targeting the UK with distinct tactics and objectives. Each poses a unique challenge, making it difficult to compare them directly.

China’s Sophisticated Espionage

China’s intelligence and military agencies now display an “eye-watering level of sophistication” in their cyber operations, Horne noted. In August 2025, the NCSC and twelve allied agencies publicly linked three Chinese companies to a global campaign targeting critical networks. This activity overlaps with what the industry tracks as Salt Typhoon.

Unlike Russian threat actors, Chinese operations are quieter and more persistent. They have shifted focus from traditional targets to edge infrastructure like routers and VPNs, according to Jamie Collier, lead threat intelligence advisor at Google Threat Intelligence Group (GTIG). This stealthy approach makes detection harder for UK organizations.

Iran’s Growing Boldness

Iran is “almost certainly” using cyber activities to suppress British individuals perceived as threats to the regime, Horne stated. The NCSC has previously warned about targeted attacks via social media messaging apps. In March, the Handala wiper campaign compromised Microsoft Intune environments and wiped devices at a key NHS supplier, showing a dangerous new direction.

Martin Riley, CTO at Bridewell, called Iran “the shifting piece.” He added that UK organizations should expect more direct Iranian or Iran-aligned targeting in the months ahead, not less.

Russia’s War-Forged Tactics

Russia continues to learn cyber lessons from its war in Ukraine. Horne explained that tactics honed in conflict are now being directed at states Russia considers hostile. The NCSC and the National Protective Security Authority observe sustained Russian hybrid activity targeting UK and European assets.

Collier noted that Russia remains the most visible and disruptive threat, mixing sophisticated espionage with a surge in pro-Russia hacktivist activity. However, Bridewell’s data suggests the current Russian effort remains concentrated on Ukraine and espionage against government targets. Direct attacks on UK operational technology are not yet common, but the risk is growing.

UK Preparedness Under the Spotlight

The readiness of UK organizations against sustained nation-state attacks is uncertain. Anthony Young, CEO of Bridewell, cautioned that most businesses are “not well prepared.” Many still struggle with basic security controls and lack full visibility across their estates. At a time when budgets are squeezed, CISOs are forced to do more with less.

Horne urged a “cultural shift” within organizations, calling on everyone—from board members to IT help desk staff—to join the cybersecurity mission. Young agreed, stating that executives need to stop paying lip service to cybersecurity and invest for the long term.

Rob Demain, CEO of e2e-assure, warned that if organizations don’t evolve their detection and response capabilities over the next 12 months, they will become “significantly under prepared.” Collier emphasized moving from a prevention-only mindset to a resilience mindset. Organizations must assume adversaries can gain initial access and focus on making their environments difficult to navigate.

For more insights on building a resilient security posture, read our guide on cyber resilience strategies for UK businesses.

AI: A Cause for Concern

Artificial intelligence is amplifying the cyber perfect storm. Following the release of Anthropic’s Claude Mythos model—which can identify and fix software vulnerabilities at speed—the UK government sent an open letter to business leaders urging them to prepare for rapid AI integration in cybersecurity.

Horne stated at CYBERUK, “Frontier AI is rapidly enabling discovery and exploitation of existing vulnerabilities at scale, illustrating how quickly it will expose where fundamentals of cyber security are still to be addressed.” Demain highlighted that zero-day attacks are becoming more common across all business sizes due to AI advancements.

Despite these threats, experts agree that basics still matter. Full visibility across all environments, 24/7 monitoring, and correct technological configuration remain some of the easiest ways to stay a hard target. Learn more about AI-driven cybersecurity threats and how to counter them.

In conclusion, the UK faces a cyber perfect storm that requires immediate action. Geopolitical tensions, nation-state attacks, and AI-driven vulnerabilities are converging. Organizations must invest in resilience, improve basic hygiene, and prepare for a future where threats are more sophisticated than ever.

CyberSecurity

PostgreSQL Patches 12-Year-Old Logical Decoding Flaw That Allowed Code Execution

Published

on

logical decoding flaw

PostgreSQL Ships Emergency Updates for a Decade-Old Security Hole

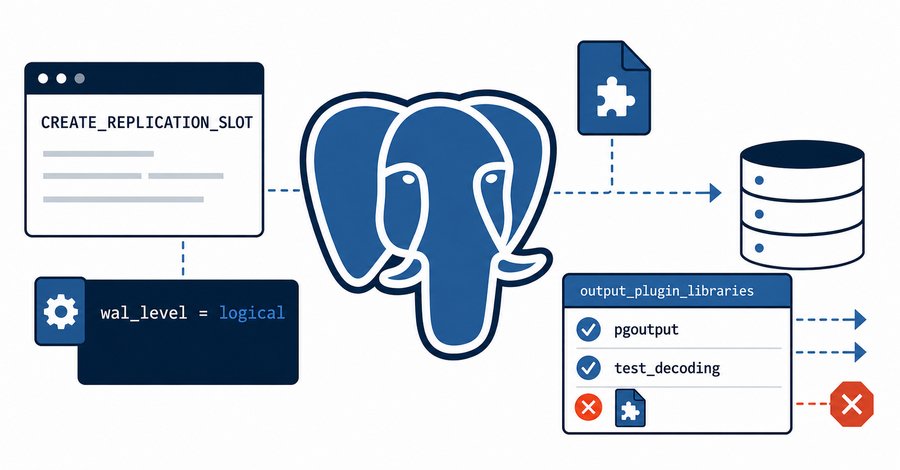
The PostgreSQL Global Development Group has pushed out urgent patch releases to close a security vulnerability that lets anyone with the REPLICATION attribute run arbitrary code as the database server’s operating-system user. The bug, tracked as CVE-2026-6471, carries a CVSS score of 7.2 — high severity by any measure.

What makes this one particularly nasty is its age. The flaw has been lurking since logical decoding was first introduced in PostgreSQL 9.4 back in 2014. That’s twelve years of exposure. Twelve years of potential exploitation for anyone who managed to obtain replication privileges.

The fix lands in versions 18.6, 17.11, 16.15, 15.19, and 14.24. If you’re running any earlier release, you’re vulnerable. No ifs, ands, or bugs.

What Exactly Is Logical Decoding, and Why Should You Care?

Logical decoding is a feature that lets you extract changes from a PostgreSQL database in a format that’s independent of the physical storage. It’s what powers streaming replication, change data capture (CDC) pipelines, and many modern data integration tools. In short, it’s the backbone of real-time data movement for countless organizations.

But here’s the catch: the vulnerability allows a user with the REPLICATION attribute — a role typically reserved for backup and replication processes — to escalate privileges and execute code as the OS user running PostgreSQL. That means an attacker who compromises a replication account could potentially take over the entire database server, read sensitive files, or even pivot to other systems on the network.

Who’s at Risk?

Any organization running PostgreSQL with logical decoding enabled and replication roles granted to non-trusted users is in the danger zone. Even if you don’t use logical decoding actively, the vulnerability exists in the code path, and a determined attacker could trigger it.

The PostgreSQL team’s advisory is clear: upgrade immediately. There are no workarounds that fully mitigate the issue, though restricting REPLICATION privileges to only the most trusted accounts can reduce your attack surface.

A Timeline of Neglect: How a 12-Year-Old Bug Survived

It’s almost unbelievable that a flaw this severe could persist for over a decade. Logical decoding was a major feature addition in 9.4, and it’s been a core part of PostgreSQL’s appeal ever since. Yet somewhere in the complex code that handles replication slots and WAL (write-ahead log) processing, a subtle bug slipped through.

Security researchers have long noted that PostgreSQL’s security record is generally solid — but this incident is a stark reminder that even the most reputable open-source projects can carry hidden landmines. The fact that it took this long to discover highlights the challenges of auditing complex, long-lived codebases.

What Should PostgreSQL Admins Do Right Now?

Here’s a practical checklist for anyone running PostgreSQL:

  • Identify your current version: SELECT version(); or check with your package manager.
  • If you’re on 14.x, 15.x, 16.x, 17.x, or 18.x, upgrade to the latest patch release listed above.
  • If you’re on an older version (e.g., 13 or below), you need to plan a major upgrade — those branches are no longer supported and won’t receive fixes.
  • Audit all roles that have the REPLICATION attribute. Revoke it from any account that doesn’t absolutely need it.
  • Review your database logs for any suspicious activity related to logical decoding or replication slots.

Don’t Forget About Your Replication Setup

If you’re using streaming replication or a tool like Debezium that relies on logical decoding, pay extra attention. Your replication slots might be active, and the vulnerability could be triggered through them. After upgrading, test your replication thoroughly to ensure nothing breaks.

Also, consider using a connection pooler or proxy to limit direct database access. It’s not a fix for this specific bug, but it’s good defense-in-depth practice.

Broader Implications for Open-Source Security

This incident raises uncomfortable questions about the sustainability of security auditing in open-source projects. PostgreSQL is maintained by a dedicated community, but it’s a massive codebase. Finding a bug that’s been hidden for 12 years requires either luck or a very thorough review.

For organizations that rely on PostgreSQL — and that’s a huge portion of the internet’s data infrastructure — this is a wake-up call. Regular security audits, prompt patching, and a strong understanding of your database’s privilege model are non-negotiable.

If you’re also using tools that interact with PostgreSQL’s logical decoding, like change data capture tools, make sure those are updated as well. And if you’re new to PostgreSQL security, check out our PostgreSQL hardening guide for baseline practices. For broader context, see how database security advisories are handled across major systems.

The bottom line: don’t wait. The exploit is public knowledge now, and attackers will be scanning for vulnerable instances. Patch your systems, tighten your roles, and hope that this 12-year-old skeleton in PostgreSQL’s closet is the last one.

Continue Reading

CyberSecurity

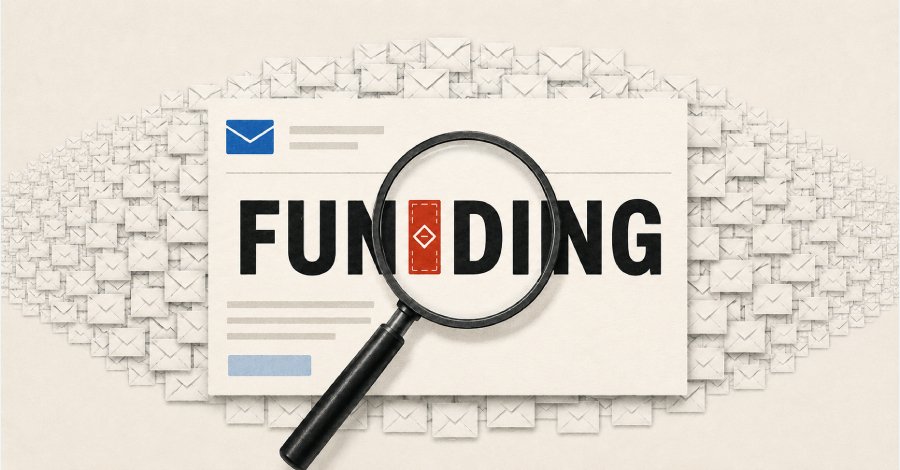
Millions of Phishing Emails Hide ‘Funding’ in Invisible Unicode to Slip Past Filters

Published

on

invisible Unicode phishing

Microsoft Warns of High-Volume Phishing Campaign

Microsoft’s security team has issued an alert about a phishing campaign that’s been blasting out millions of emails. The trick? Invisible Unicode tag characters that split financial lure words like ‘funding’ to dodge email filters.

Instead of hiding instructions from humans while exposing them to AI models, the attackers used these invisible characters to break up keywords. That way, the filters never see the full word — but the recipient’s email client renders it seamlessly.

How the Invisible Unicode Attack Works

Unicode tag characters are normally used for language tagging in plain text. They’re invisible in most rendering engines. Attackers inserted them mid-word, so ‘funding’ becomes ‘f-u-n-d-i-n-g’ with invisible tags between each letter.

Filters that scan for exact strings don’t match. The email lands in the inbox looking perfectly normal. It’s a clever piece of social engineering that targets the gap between what machines parse and what humans read.

The Role of AI in Detection

Microsoft’s research team noted that while AI models can often spot these anomalies, the attackers deliberately avoided that route. They weren’t trying to trick AI — they wanted to slip past traditional signature-based filters that haven’t caught up to Unicode obfuscation.

This marks a shift in tactics. Earlier campaigns used Unicode to hide malicious instructions from human reviewers while keeping them visible to AI. This one flips the script entirely.

Why Financial Lure Words Matter

Words like ‘funding’, ‘transfer’, and ‘invoice’ are common hooks in business email compromise (BEC) scams. By splitting them, attackers ensure their emails don’t trigger the same automated checks that would normally flag them.

  • Filter evasion: Splitting keywords means regex patterns and string matches fail.
  • Human perception: Invisible characters don’t alter how the email looks to a recipient.
  • Scale: Microsoft describes this as high-volume, meaning millions of emails are involved.

The campaign appears to target organizations that handle financial transactions — payroll departments, accounts payable teams, and CFOs.

How to Protect Against Unicode Phishing

Email security teams need to update their detection rules. Look for emails that contain Unicode tag characters (U+E0000 to U+E007F) in suspicious positions, especially inside common financial keywords.

Regular users should be cautious of unexpected emails asking for wire transfers or payment changes, even if they look legitimate. Verify requests through a second channel — a phone call, not a reply email.

For more on protecting yourself, check out our guide on recognizing phishing email signs. If you’re dealing with a potential breach, our article on incident response steps for small businesses can help you react quickly.

Technical Mitigations

Administrators can configure their email gateways to either strip or flag Unicode tag characters in incoming messages. Microsoft Defender for Office 365 has also been updated to detect this pattern, but organizations using other filters should test their own systems.

Security researchers recommend adding decoy keywords to honeypots — traps that catch attackers when they use the same obfuscation technique.

The Bottom Line

This campaign is a reminder that email filters are only as good as their understanding of attacker tricks. Invisible Unicode is not new — but using it to split lure words for mass distribution is a fresh twist that many defenses aren’t ready for.

Stay alert. If an email asks for money or sensitive data, scrutinize it — even if it looks perfect. And if you’re in IT, audit your mail flow for Unicode anomalies before the next wave hits.

Continue Reading

CyberSecurity

Microsoft Cloud Patches, 5,000 Hacked Dropbox Accounts, and a $1.1B Security Startup: What You Missed

Published

on

Microsoft cloud patches

The Week’s Under-the-Radar Security Stories

Some stories don’t get the headline treatment they deserve. They still matter, though. This week’s quiet-but-significant batch includes a wave of cloud patches from Microsoft, a credential-stuffing attack on Dropbox, and a cybersecurity startup hitting unicorn status.

Here’s what you need to know.

Microsoft Rolls Out Patches for Cloud Services

Microsoft has been busy behind the scenes. The company pushed out fixes for several of its cloud offerings, addressing vulnerabilities that could have given attackers a foothold in enterprise environments.

The patches cover a range of services, though Microsoft hasn’t disclosed every detail. What’s clear is that IT teams should treat these updates as priority. Cloud misconfigurations and unpatched flaws remain a top attack vector, and this is a reminder that even the biggest providers need constant upkeep.

For admins, the takeaway is straightforward: check your Microsoft cloud security dashboard, review the latest advisories, and apply the updates before they become a problem. Delaying patches in a cloud environment is a gamble, and the house usually wins.

What the Patches Target

Microsoft’s advisory points to vulnerabilities in Azure and related services. Specifics are sparse, but the company’s track record suggests these could range from privilege escalation to information disclosure. If you’re running any Microsoft cloud workload, the official security update guide is your first stop.

5,000 Dropbox Accounts Hacked via Credential Stuffing

Dropbox confirmed that attackers compromised roughly 5,000 user accounts. The method? Credential stuffing — using usernames and passwords stolen from other breaches to break into accounts where people reuse passwords.

This isn’t a breach of Dropbox’s own systems. The company says its infrastructure wasn’t compromised. Instead, the attackers leveraged the all-too-common habit of password reuse. Once they had valid credentials from elsewhere, they simply tried them on Dropbox.

Dropbox has reset passwords for affected users and is rolling out additional protections. But the incident underscores a persistent problem: credential stuffing attacks remain one of the most effective ways for hackers to get in. No fancy exploits needed, just a list of leaked passwords and a bit of patience.

How to Protect Yourself

  • Use a unique password for every account. Yes, every single one.
  • Enable two-factor authentication, especially on cloud storage and email.
  • Check haveibeenpwned.com to see if your credentials have been exposed.
  • If you’re a Dropbox user, change your password now, even if you weren’t affected.

It’s tedious, but it works. The hackers who did this weren’t geniuses — they were just counting on people to make the same mistake twice.

Guardio Hits $1.1 Billion Valuation

In brighter news, Guardio, a browser security startup, has reached a valuation of $1.1 billion. The company, which focuses on protecting consumers from phishing, malware, and malicious extensions, has been growing quietly but steadily.

Guardio’s approach is simple: a lightweight browser extension that blocks threats before they reach the user. It’s a consumer-focused product, but the underlying tech has broader implications. As more people work from home, the browser has become the new perimeter.

The Guardio funding round signals that investors see value in endpoint protection that doesn’t require a degree in cybersecurity to operate. That’s a good sign for the industry, and an even better one for users who just want to browse without getting hacked.

Why These Stories Matter

On the surface, these three items seem disconnected. A cloud patch, a credential stuffing attack, and a funding round — what’s the thread?

It’s this: security is a moving target. Microsoft’s patches show that even the giants are constantly fixing holes. The Dropbox incident shows that human behavior — password reuse, ignored 2FA — often undoes even the best technical defenses. And Guardio’s valuation shows that the market rewards products that make security accessible.

None of these stories will dominate tomorrow’s headlines. But together, they paint a picture of an industry that’s always fighting, always adapting, and always finding new ways to protect users. That’s worth paying attention to, even if it doesn’t make the front page.

Stay patched, stay vigilant, and for heaven’s sake, stop reusing your passwords.

Continue Reading

Trending