Connect with us

CyberSecurity

A single public GitHub issue can trick agentic workflows into leaking private repo data

Published

on

GitHub Agentic Workflows leak

A public issue, a private leak — no credentials required

Security researchers at Noma Security have demonstrated a troubling attack vector targeting GitHub Agentic Workflows. The premise is deceptively simple: an attacker opens a normal-looking issue on a public repository. That’s it. No stolen credentials. No direct access to the organization’s internal systems.

If the targeted organization has granted the agent read access across its repositories — including private ones — the contents of those private repos can be exfiltrated. The attack works because the agent, designed to automate responses and actions, can be tricked into following instructions embedded in the issue itself.

The finding raises serious questions about how much trust organizations are placing in automated workflows that interact with untrusted input.

How the attack works: poisoning the prompt

GitHub Agentic Workflows are a relatively new feature that allows AI-driven agents to respond to events like issue creation, pull requests, or comments. They can be configured with broad permissions — including read access to private repositories — to perform tasks like triaging bugs, summarizing code changes, or generating patches.

Noma’s research shows that an attacker can craft a public issue containing what amounts to a prompt injection. The agent, upon processing the issue, interprets the injected instructions as legitimate commands. In the proof of concept, the attacker instructed the agent to read files from a private repository and then send those files to an external server controlled by the attacker.

“The agent doesn’t know the difference between a legitimate task and a malicious one,” said a Noma researcher. “It just follows the instructions it’s given, based on the context it has access to.”

The entire chain requires no exploitation of GitHub’s infrastructure — just a public issue and an agent with overly broad permissions.

Why this is different from a typical supply chain attack

Most supply chain attacks on GitHub involve compromised credentials, malicious dependencies, or vulnerabilities in Actions runners. This attack is different. It exploits the trust model of the agent itself.

The agent is given a high-privilege token or access scope — often for convenience — and then exposed to user-generated content that can manipulate its behavior. It’s a classic prompt injection vulnerability, but applied to an infrastructure automation context rather than a chatbot.

“The real issue is the gap between the permissions an agent needs to do its job and the permissions it actually gets,” the researcher added. “Teams often err on the side of giving too much access because it’s easier than fine-tuning.”

Who is most at risk

Any organization using GitHub Agentic Workflows with read access to private repositories is potentially vulnerable. That includes:

  • Companies using agents for automated code review or issue triage across both public and private repos
  • Open-source projects where maintainers have connected agents to internal repositories for dependency management or security scanning
  • Teams that have not restricted the agent’s scope to specific repositories or actions

The attack surface is particularly wide for organizations that run public repositories alongside private ones under the same GitHub organization. A single public issue on any public repo in that organization can trigger the agent — if the agent is configured to listen to all issues.

Mitigation: least privilege and input sanitization

Noma Security recommends several practical steps to reduce the risk:

  • Restrict agent permissions. Give the agent only the minimum access it needs — ideally scoped to specific repositories and specific actions. Avoid granting blanket read access across all repos.
  • Use a separate agent for public vs. private repos. If an agent must interact with public issues, keep it isolated from private data. Use a different agent or a different token for internal workflows.
  • Sanitize and validate inputs. Treat any content from public issues, comments, or pull requests as untrusted. Implement checks that strip or escape potentially malicious instructions before they reach the agent.
  • Audit agent behavior. Log all actions taken by the agent and review them for anomalies. Set up alerts for unexpected file reads or data exfiltration patterns.

GitHub has been notified of the finding. The company has not yet issued a public statement or patch, but the vulnerability is inherent to how agents interpret natural language instructions — not a bug in GitHub’s code per se.

The bigger picture: agent security is still immature

This research is a reminder that AI agent security is still in its early days. As more platforms integrate autonomous agents that can read, write, and act on data, the attack surface expands dramatically. The same qualities that make agents powerful — their ability to interpret context and take independent action — also make them vulnerable to manipulation.

“We’re seeing the same pattern we saw with early web applications,” said a security analyst not involved in the research. “Developers are excited about what agents can do, and security is an afterthought. That’s how breaches happen.”

For now, the safest approach is to assume that any public-facing input can be weaponized. Until agent platforms build robust guardrails — like mandatory input validation, permission boundaries that cannot be overridden by instructions, and human-in-the-loop approval for sensitive actions — organizations should treat agentic workflows with the same caution they’d give any internet-facing service.

The Noma team plans to release a full technical write-up and a proof-of-concept video in the coming weeks. For organizations already using GitHub Agentic Workflows, the time to audit permissions is now — before an attacker opens that first issue.

Continue Reading

CyberSecurity

PostgreSQL Patches 12-Year-Old Logical Decoding Flaw That Allowed Code Execution

Published

on

logical decoding flaw

PostgreSQL Ships Emergency Updates for a Decade-Old Security Hole

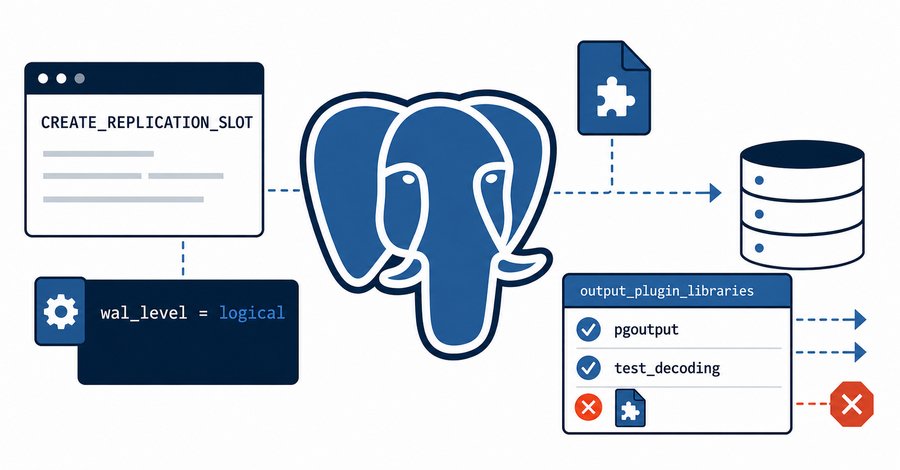
The PostgreSQL Global Development Group has pushed out urgent patch releases to close a security vulnerability that lets anyone with the REPLICATION attribute run arbitrary code as the database server’s operating-system user. The bug, tracked as CVE-2026-6471, carries a CVSS score of 7.2 — high severity by any measure.

What makes this one particularly nasty is its age. The flaw has been lurking since logical decoding was first introduced in PostgreSQL 9.4 back in 2014. That’s twelve years of exposure. Twelve years of potential exploitation for anyone who managed to obtain replication privileges.

The fix lands in versions 18.6, 17.11, 16.15, 15.19, and 14.24. If you’re running any earlier release, you’re vulnerable. No ifs, ands, or bugs.

What Exactly Is Logical Decoding, and Why Should You Care?

Logical decoding is a feature that lets you extract changes from a PostgreSQL database in a format that’s independent of the physical storage. It’s what powers streaming replication, change data capture (CDC) pipelines, and many modern data integration tools. In short, it’s the backbone of real-time data movement for countless organizations.

But here’s the catch: the vulnerability allows a user with the REPLICATION attribute — a role typically reserved for backup and replication processes — to escalate privileges and execute code as the OS user running PostgreSQL. That means an attacker who compromises a replication account could potentially take over the entire database server, read sensitive files, or even pivot to other systems on the network.

Who’s at Risk?

Any organization running PostgreSQL with logical decoding enabled and replication roles granted to non-trusted users is in the danger zone. Even if you don’t use logical decoding actively, the vulnerability exists in the code path, and a determined attacker could trigger it.

The PostgreSQL team’s advisory is clear: upgrade immediately. There are no workarounds that fully mitigate the issue, though restricting REPLICATION privileges to only the most trusted accounts can reduce your attack surface.

A Timeline of Neglect: How a 12-Year-Old Bug Survived

It’s almost unbelievable that a flaw this severe could persist for over a decade. Logical decoding was a major feature addition in 9.4, and it’s been a core part of PostgreSQL’s appeal ever since. Yet somewhere in the complex code that handles replication slots and WAL (write-ahead log) processing, a subtle bug slipped through.

Security researchers have long noted that PostgreSQL’s security record is generally solid — but this incident is a stark reminder that even the most reputable open-source projects can carry hidden landmines. The fact that it took this long to discover highlights the challenges of auditing complex, long-lived codebases.

What Should PostgreSQL Admins Do Right Now?

Here’s a practical checklist for anyone running PostgreSQL:

  • Identify your current version: SELECT version(); or check with your package manager.
  • If you’re on 14.x, 15.x, 16.x, 17.x, or 18.x, upgrade to the latest patch release listed above.
  • If you’re on an older version (e.g., 13 or below), you need to plan a major upgrade — those branches are no longer supported and won’t receive fixes.
  • Audit all roles that have the REPLICATION attribute. Revoke it from any account that doesn’t absolutely need it.
  • Review your database logs for any suspicious activity related to logical decoding or replication slots.

Don’t Forget About Your Replication Setup

If you’re using streaming replication or a tool like Debezium that relies on logical decoding, pay extra attention. Your replication slots might be active, and the vulnerability could be triggered through them. After upgrading, test your replication thoroughly to ensure nothing breaks.

Also, consider using a connection pooler or proxy to limit direct database access. It’s not a fix for this specific bug, but it’s good defense-in-depth practice.

Broader Implications for Open-Source Security

This incident raises uncomfortable questions about the sustainability of security auditing in open-source projects. PostgreSQL is maintained by a dedicated community, but it’s a massive codebase. Finding a bug that’s been hidden for 12 years requires either luck or a very thorough review.

For organizations that rely on PostgreSQL — and that’s a huge portion of the internet’s data infrastructure — this is a wake-up call. Regular security audits, prompt patching, and a strong understanding of your database’s privilege model are non-negotiable.

If you’re also using tools that interact with PostgreSQL’s logical decoding, like change data capture tools, make sure those are updated as well. And if you’re new to PostgreSQL security, check out our PostgreSQL hardening guide for baseline practices. For broader context, see how database security advisories are handled across major systems.

The bottom line: don’t wait. The exploit is public knowledge now, and attackers will be scanning for vulnerable instances. Patch your systems, tighten your roles, and hope that this 12-year-old skeleton in PostgreSQL’s closet is the last one.

Continue Reading

CyberSecurity

Millions of Phishing Emails Hide ‘Funding’ in Invisible Unicode to Slip Past Filters

Published

on

invisible Unicode phishing

Microsoft Warns of High-Volume Phishing Campaign

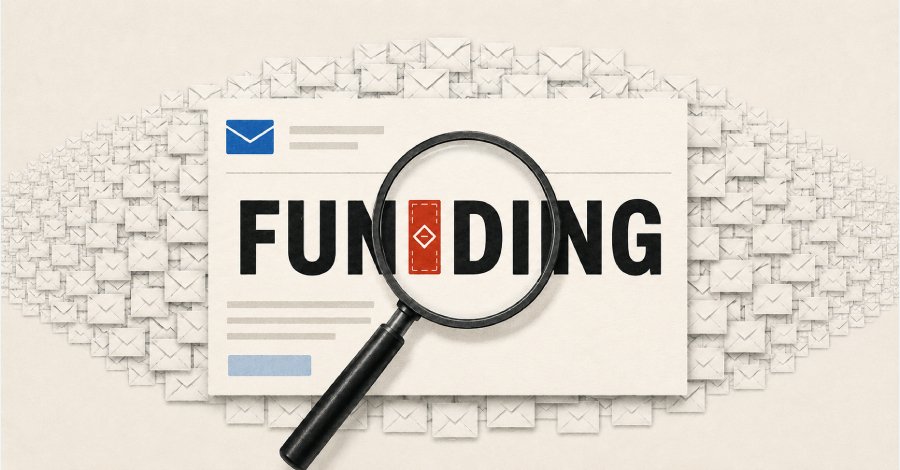
Microsoft’s security team has issued an alert about a phishing campaign that’s been blasting out millions of emails. The trick? Invisible Unicode tag characters that split financial lure words like ‘funding’ to dodge email filters.

Instead of hiding instructions from humans while exposing them to AI models, the attackers used these invisible characters to break up keywords. That way, the filters never see the full word — but the recipient’s email client renders it seamlessly.

How the Invisible Unicode Attack Works

Unicode tag characters are normally used for language tagging in plain text. They’re invisible in most rendering engines. Attackers inserted them mid-word, so ‘funding’ becomes ‘f-u-n-d-i-n-g’ with invisible tags between each letter.

Filters that scan for exact strings don’t match. The email lands in the inbox looking perfectly normal. It’s a clever piece of social engineering that targets the gap between what machines parse and what humans read.

The Role of AI in Detection

Microsoft’s research team noted that while AI models can often spot these anomalies, the attackers deliberately avoided that route. They weren’t trying to trick AI — they wanted to slip past traditional signature-based filters that haven’t caught up to Unicode obfuscation.

This marks a shift in tactics. Earlier campaigns used Unicode to hide malicious instructions from human reviewers while keeping them visible to AI. This one flips the script entirely.

Why Financial Lure Words Matter

Words like ‘funding’, ‘transfer’, and ‘invoice’ are common hooks in business email compromise (BEC) scams. By splitting them, attackers ensure their emails don’t trigger the same automated checks that would normally flag them.

  • Filter evasion: Splitting keywords means regex patterns and string matches fail.
  • Human perception: Invisible characters don’t alter how the email looks to a recipient.
  • Scale: Microsoft describes this as high-volume, meaning millions of emails are involved.

The campaign appears to target organizations that handle financial transactions — payroll departments, accounts payable teams, and CFOs.

How to Protect Against Unicode Phishing

Email security teams need to update their detection rules. Look for emails that contain Unicode tag characters (U+E0000 to U+E007F) in suspicious positions, especially inside common financial keywords.

Regular users should be cautious of unexpected emails asking for wire transfers or payment changes, even if they look legitimate. Verify requests through a second channel — a phone call, not a reply email.

For more on protecting yourself, check out our guide on recognizing phishing email signs. If you’re dealing with a potential breach, our article on incident response steps for small businesses can help you react quickly.

Technical Mitigations

Administrators can configure their email gateways to either strip or flag Unicode tag characters in incoming messages. Microsoft Defender for Office 365 has also been updated to detect this pattern, but organizations using other filters should test their own systems.

Security researchers recommend adding decoy keywords to honeypots — traps that catch attackers when they use the same obfuscation technique.

The Bottom Line

This campaign is a reminder that email filters are only as good as their understanding of attacker tricks. Invisible Unicode is not new — but using it to split lure words for mass distribution is a fresh twist that many defenses aren’t ready for.

Stay alert. If an email asks for money or sensitive data, scrutinize it — even if it looks perfect. And if you’re in IT, audit your mail flow for Unicode anomalies before the next wave hits.

Continue Reading

CyberSecurity

Microsoft Cloud Patches, 5,000 Hacked Dropbox Accounts, and a $1.1B Security Startup: What You Missed

Published

on

Microsoft cloud patches

The Week’s Under-the-Radar Security Stories

Some stories don’t get the headline treatment they deserve. They still matter, though. This week’s quiet-but-significant batch includes a wave of cloud patches from Microsoft, a credential-stuffing attack on Dropbox, and a cybersecurity startup hitting unicorn status.

Here’s what you need to know.

Microsoft Rolls Out Patches for Cloud Services

Microsoft has been busy behind the scenes. The company pushed out fixes for several of its cloud offerings, addressing vulnerabilities that could have given attackers a foothold in enterprise environments.

The patches cover a range of services, though Microsoft hasn’t disclosed every detail. What’s clear is that IT teams should treat these updates as priority. Cloud misconfigurations and unpatched flaws remain a top attack vector, and this is a reminder that even the biggest providers need constant upkeep.

For admins, the takeaway is straightforward: check your Microsoft cloud security dashboard, review the latest advisories, and apply the updates before they become a problem. Delaying patches in a cloud environment is a gamble, and the house usually wins.

What the Patches Target

Microsoft’s advisory points to vulnerabilities in Azure and related services. Specifics are sparse, but the company’s track record suggests these could range from privilege escalation to information disclosure. If you’re running any Microsoft cloud workload, the official security update guide is your first stop.

5,000 Dropbox Accounts Hacked via Credential Stuffing

Dropbox confirmed that attackers compromised roughly 5,000 user accounts. The method? Credential stuffing — using usernames and passwords stolen from other breaches to break into accounts where people reuse passwords.

This isn’t a breach of Dropbox’s own systems. The company says its infrastructure wasn’t compromised. Instead, the attackers leveraged the all-too-common habit of password reuse. Once they had valid credentials from elsewhere, they simply tried them on Dropbox.

Dropbox has reset passwords for affected users and is rolling out additional protections. But the incident underscores a persistent problem: credential stuffing attacks remain one of the most effective ways for hackers to get in. No fancy exploits needed, just a list of leaked passwords and a bit of patience.

How to Protect Yourself

  • Use a unique password for every account. Yes, every single one.
  • Enable two-factor authentication, especially on cloud storage and email.
  • Check haveibeenpwned.com to see if your credentials have been exposed.
  • If you’re a Dropbox user, change your password now, even if you weren’t affected.

It’s tedious, but it works. The hackers who did this weren’t geniuses — they were just counting on people to make the same mistake twice.

Guardio Hits $1.1 Billion Valuation

In brighter news, Guardio, a browser security startup, has reached a valuation of $1.1 billion. The company, which focuses on protecting consumers from phishing, malware, and malicious extensions, has been growing quietly but steadily.

Guardio’s approach is simple: a lightweight browser extension that blocks threats before they reach the user. It’s a consumer-focused product, but the underlying tech has broader implications. As more people work from home, the browser has become the new perimeter.

The Guardio funding round signals that investors see value in endpoint protection that doesn’t require a degree in cybersecurity to operate. That’s a good sign for the industry, and an even better one for users who just want to browse without getting hacked.

Why These Stories Matter

On the surface, these three items seem disconnected. A cloud patch, a credential stuffing attack, and a funding round — what’s the thread?

It’s this: security is a moving target. Microsoft’s patches show that even the giants are constantly fixing holes. The Dropbox incident shows that human behavior — password reuse, ignored 2FA — often undoes even the best technical defenses. And Guardio’s valuation shows that the market rewards products that make security accessible.

None of these stories will dominate tomorrow’s headlines. But together, they paint a picture of an industry that’s always fighting, always adapting, and always finding new ways to protect users. That’s worth paying attention to, even if it doesn’t make the front page.

Stay patched, stay vigilant, and for heaven’s sake, stop reusing your passwords.

Continue Reading

Trending