Connect with us

CyberSecurity

Beyond IT: North Korean Job Fraud Quietly Infiltrates Healthcare and Sales

Published

on

North Korean job fraud

The Threat Is No Longer Just About Code

For years, the story was simple: North Korean operatives posed as remote IT contractors, slipping into Western tech firms to steal code and earn hard currency for the regime. That playbook has changed. Recent investigations have uncovered suspected DPRK-linked workers embedded in sales, marketing, and even the medical profession.

This isn’t a minor shift. It’s a strategic expansion of what security researchers call the IT worker scheme — and it means the hiring manager at your clinic or your B2B sales team could be the next target.

How the Scheme Works

The DPRK’s operatives don’t show up with a badge. They work through a network of front companies, fake identities, and overseas intermediaries. A candidate might have a polished LinkedIn profile, years of fabricated experience, and a flawless interview manner. The catch? The person on the call isn’t the person who’ll be doing the work.

In many cases, a U.S.-based or third-country national takes the interview, while a North Korean operative performs the actual job duties remotely. The salary is funneled back to Pyongyang, often via cryptocurrency or shell accounts.

Why Healthcare and Sales?

Healthcare offers access to sensitive patient data and research — a goldmine for intelligence agencies. Sales roles, meanwhile, provide a foot in the door at hundreds of companies, offering a vantage point for corporate espionage and supply chain infiltration. These sectors also tend to have less rigorous vetting than government or defense contracting.

The result is a quieter, more insidious threat. A sales rep with access to client lists. A medical coder with access to records. Neither raises an eyebrow.

Real-World Cases and Red Flags

Investigations by firms like Mandiant and others have traced specific incidents where DPRK operatives successfully secured roles outside IT. In one case, a suspected operative was hired for a sales position after a series of video interviews with a stand-in. In another, a medical data entry role was filled by someone using a stolen U.S. identity.

So what should employers watch for? Here’s a practical checklist:

  • Video interview mismatches: The person on screen looks different from their ID photo, or their lips don’t sync with the audio.
  • Reluctance to turn on the camera: Persistent excuses about hardware issues or poor internet.
  • Overly generic resumes: Experience listed at obscure companies that have no digital footprint.
  • Requests for specific payment methods: Cryptocurrency, prepaid cards, or wiring to third-party accounts.
  • Inconsistent time zones: A candidate claiming to be in the U.S. but always available at 3 a.m. local time.

None of these are smoking guns alone. But together, they warrant a deeper look.

What Companies Can Do Right Now

The good news? Mitigation is possible. Start with identity verification that goes beyond a cursory background check. Use live video interviews with a second interviewer present. Check references manually — call the actual company, not the number on the resume.

For remote-first organizations, consider deploying endpoint monitoring that flags unusual data access patterns. A sales rep pulling thousands of records at 2 a.m. is a red flag, regardless of their job title. And for healthcare employers, compliance with HIPAA isn’t just a legal requirement — it’s a front-line defense against insider threats.

Training matters too. Your HR team should know what the IT worker scheme looks like, even if they’ve never heard the term. A short briefing on these tactics can prevent a costly hire.

The Bigger Picture

This expansion signals that North Korea is adapting to Western defenses. As tech companies tighten their vetting, the regime’s operatives are simply moving to softer targets. Healthcare and sales are just the latest stops on that path.

The threat isn’t going away. But awareness is half the battle. If you’re hiring for a role that touches sensitive data — in any sector — treat the interview process like a security review, not just a talent search.

Stay updated on the latest tactics in our guide to remote work security best practices, and check out our breakdown of insider threat detection strategies for more actionable advice. For a deeper dive into the DPRK’s methods, see our analysis of state-sponsored cyber espionage trends.

Continue Reading

CyberSecurity

PostgreSQL Patches 12-Year-Old Logical Decoding Flaw That Allowed Code Execution

Published

on

logical decoding flaw

PostgreSQL Ships Emergency Updates for a Decade-Old Security Hole

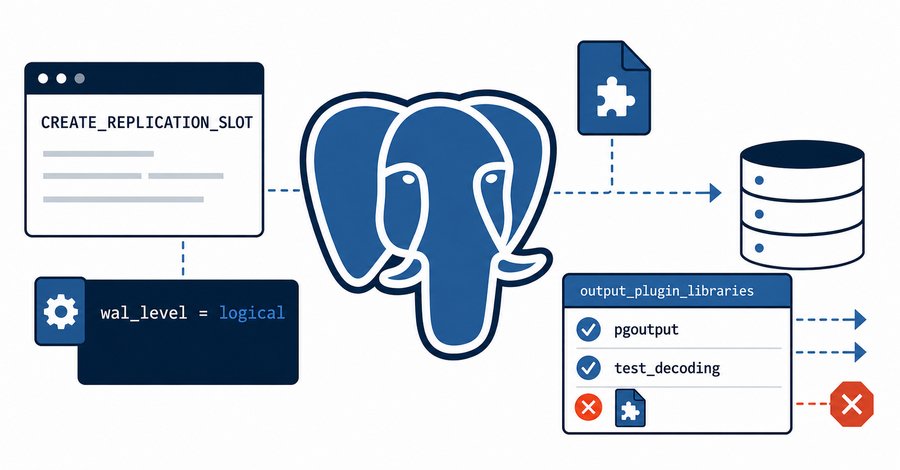
The PostgreSQL Global Development Group has pushed out urgent patch releases to close a security vulnerability that lets anyone with the REPLICATION attribute run arbitrary code as the database server’s operating-system user. The bug, tracked as CVE-2026-6471, carries a CVSS score of 7.2 — high severity by any measure.

What makes this one particularly nasty is its age. The flaw has been lurking since logical decoding was first introduced in PostgreSQL 9.4 back in 2014. That’s twelve years of exposure. Twelve years of potential exploitation for anyone who managed to obtain replication privileges.

The fix lands in versions 18.6, 17.11, 16.15, 15.19, and 14.24. If you’re running any earlier release, you’re vulnerable. No ifs, ands, or bugs.

What Exactly Is Logical Decoding, and Why Should You Care?

Logical decoding is a feature that lets you extract changes from a PostgreSQL database in a format that’s independent of the physical storage. It’s what powers streaming replication, change data capture (CDC) pipelines, and many modern data integration tools. In short, it’s the backbone of real-time data movement for countless organizations.

But here’s the catch: the vulnerability allows a user with the REPLICATION attribute — a role typically reserved for backup and replication processes — to escalate privileges and execute code as the OS user running PostgreSQL. That means an attacker who compromises a replication account could potentially take over the entire database server, read sensitive files, or even pivot to other systems on the network.

Who’s at Risk?

Any organization running PostgreSQL with logical decoding enabled and replication roles granted to non-trusted users is in the danger zone. Even if you don’t use logical decoding actively, the vulnerability exists in the code path, and a determined attacker could trigger it.

The PostgreSQL team’s advisory is clear: upgrade immediately. There are no workarounds that fully mitigate the issue, though restricting REPLICATION privileges to only the most trusted accounts can reduce your attack surface.

A Timeline of Neglect: How a 12-Year-Old Bug Survived

It’s almost unbelievable that a flaw this severe could persist for over a decade. Logical decoding was a major feature addition in 9.4, and it’s been a core part of PostgreSQL’s appeal ever since. Yet somewhere in the complex code that handles replication slots and WAL (write-ahead log) processing, a subtle bug slipped through.

Security researchers have long noted that PostgreSQL’s security record is generally solid — but this incident is a stark reminder that even the most reputable open-source projects can carry hidden landmines. The fact that it took this long to discover highlights the challenges of auditing complex, long-lived codebases.

What Should PostgreSQL Admins Do Right Now?

Here’s a practical checklist for anyone running PostgreSQL:

  • Identify your current version: SELECT version(); or check with your package manager.
  • If you’re on 14.x, 15.x, 16.x, 17.x, or 18.x, upgrade to the latest patch release listed above.
  • If you’re on an older version (e.g., 13 or below), you need to plan a major upgrade — those branches are no longer supported and won’t receive fixes.
  • Audit all roles that have the REPLICATION attribute. Revoke it from any account that doesn’t absolutely need it.
  • Review your database logs for any suspicious activity related to logical decoding or replication slots.

Don’t Forget About Your Replication Setup

If you’re using streaming replication or a tool like Debezium that relies on logical decoding, pay extra attention. Your replication slots might be active, and the vulnerability could be triggered through them. After upgrading, test your replication thoroughly to ensure nothing breaks.

Also, consider using a connection pooler or proxy to limit direct database access. It’s not a fix for this specific bug, but it’s good defense-in-depth practice.

Broader Implications for Open-Source Security

This incident raises uncomfortable questions about the sustainability of security auditing in open-source projects. PostgreSQL is maintained by a dedicated community, but it’s a massive codebase. Finding a bug that’s been hidden for 12 years requires either luck or a very thorough review.

For organizations that rely on PostgreSQL — and that’s a huge portion of the internet’s data infrastructure — this is a wake-up call. Regular security audits, prompt patching, and a strong understanding of your database’s privilege model are non-negotiable.

If you’re also using tools that interact with PostgreSQL’s logical decoding, like change data capture tools, make sure those are updated as well. And if you’re new to PostgreSQL security, check out our PostgreSQL hardening guide for baseline practices. For broader context, see how database security advisories are handled across major systems.

The bottom line: don’t wait. The exploit is public knowledge now, and attackers will be scanning for vulnerable instances. Patch your systems, tighten your roles, and hope that this 12-year-old skeleton in PostgreSQL’s closet is the last one.

Continue Reading

CyberSecurity

Millions of Phishing Emails Hide ‘Funding’ in Invisible Unicode to Slip Past Filters

Published

on

invisible Unicode phishing

Microsoft Warns of High-Volume Phishing Campaign

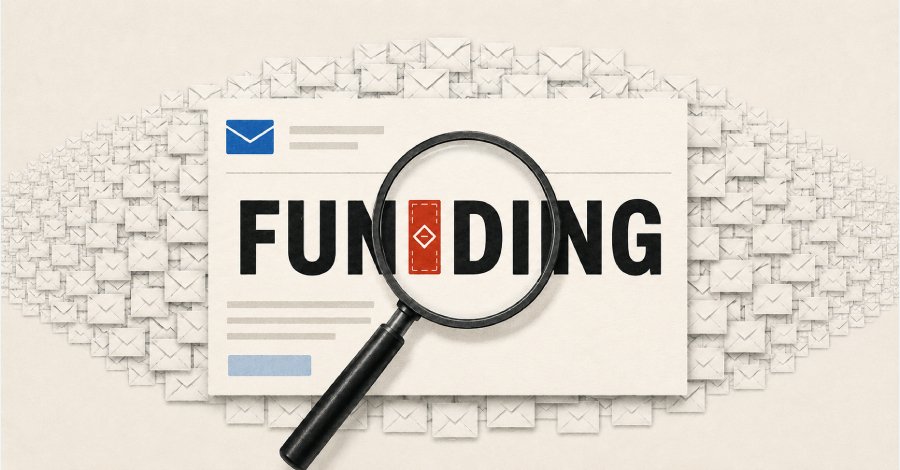
Microsoft’s security team has issued an alert about a phishing campaign that’s been blasting out millions of emails. The trick? Invisible Unicode tag characters that split financial lure words like ‘funding’ to dodge email filters.

Instead of hiding instructions from humans while exposing them to AI models, the attackers used these invisible characters to break up keywords. That way, the filters never see the full word — but the recipient’s email client renders it seamlessly.

How the Invisible Unicode Attack Works

Unicode tag characters are normally used for language tagging in plain text. They’re invisible in most rendering engines. Attackers inserted them mid-word, so ‘funding’ becomes ‘f-u-n-d-i-n-g’ with invisible tags between each letter.

Filters that scan for exact strings don’t match. The email lands in the inbox looking perfectly normal. It’s a clever piece of social engineering that targets the gap between what machines parse and what humans read.

The Role of AI in Detection

Microsoft’s research team noted that while AI models can often spot these anomalies, the attackers deliberately avoided that route. They weren’t trying to trick AI — they wanted to slip past traditional signature-based filters that haven’t caught up to Unicode obfuscation.

This marks a shift in tactics. Earlier campaigns used Unicode to hide malicious instructions from human reviewers while keeping them visible to AI. This one flips the script entirely.

Why Financial Lure Words Matter

Words like ‘funding’, ‘transfer’, and ‘invoice’ are common hooks in business email compromise (BEC) scams. By splitting them, attackers ensure their emails don’t trigger the same automated checks that would normally flag them.

  • Filter evasion: Splitting keywords means regex patterns and string matches fail.
  • Human perception: Invisible characters don’t alter how the email looks to a recipient.
  • Scale: Microsoft describes this as high-volume, meaning millions of emails are involved.

The campaign appears to target organizations that handle financial transactions — payroll departments, accounts payable teams, and CFOs.

How to Protect Against Unicode Phishing

Email security teams need to update their detection rules. Look for emails that contain Unicode tag characters (U+E0000 to U+E007F) in suspicious positions, especially inside common financial keywords.

Regular users should be cautious of unexpected emails asking for wire transfers or payment changes, even if they look legitimate. Verify requests through a second channel — a phone call, not a reply email.

For more on protecting yourself, check out our guide on recognizing phishing email signs. If you’re dealing with a potential breach, our article on incident response steps for small businesses can help you react quickly.

Technical Mitigations

Administrators can configure their email gateways to either strip or flag Unicode tag characters in incoming messages. Microsoft Defender for Office 365 has also been updated to detect this pattern, but organizations using other filters should test their own systems.

Security researchers recommend adding decoy keywords to honeypots — traps that catch attackers when they use the same obfuscation technique.

The Bottom Line

This campaign is a reminder that email filters are only as good as their understanding of attacker tricks. Invisible Unicode is not new — but using it to split lure words for mass distribution is a fresh twist that many defenses aren’t ready for.

Stay alert. If an email asks for money or sensitive data, scrutinize it — even if it looks perfect. And if you’re in IT, audit your mail flow for Unicode anomalies before the next wave hits.

Continue Reading

CyberSecurity

Microsoft Cloud Patches, 5,000 Hacked Dropbox Accounts, and a $1.1B Security Startup: What You Missed

Published

on

Microsoft cloud patches

The Week’s Under-the-Radar Security Stories

Some stories don’t get the headline treatment they deserve. They still matter, though. This week’s quiet-but-significant batch includes a wave of cloud patches from Microsoft, a credential-stuffing attack on Dropbox, and a cybersecurity startup hitting unicorn status.

Here’s what you need to know.

Microsoft Rolls Out Patches for Cloud Services

Microsoft has been busy behind the scenes. The company pushed out fixes for several of its cloud offerings, addressing vulnerabilities that could have given attackers a foothold in enterprise environments.

The patches cover a range of services, though Microsoft hasn’t disclosed every detail. What’s clear is that IT teams should treat these updates as priority. Cloud misconfigurations and unpatched flaws remain a top attack vector, and this is a reminder that even the biggest providers need constant upkeep.

For admins, the takeaway is straightforward: check your Microsoft cloud security dashboard, review the latest advisories, and apply the updates before they become a problem. Delaying patches in a cloud environment is a gamble, and the house usually wins.

What the Patches Target

Microsoft’s advisory points to vulnerabilities in Azure and related services. Specifics are sparse, but the company’s track record suggests these could range from privilege escalation to information disclosure. If you’re running any Microsoft cloud workload, the official security update guide is your first stop.

5,000 Dropbox Accounts Hacked via Credential Stuffing

Dropbox confirmed that attackers compromised roughly 5,000 user accounts. The method? Credential stuffing — using usernames and passwords stolen from other breaches to break into accounts where people reuse passwords.

This isn’t a breach of Dropbox’s own systems. The company says its infrastructure wasn’t compromised. Instead, the attackers leveraged the all-too-common habit of password reuse. Once they had valid credentials from elsewhere, they simply tried them on Dropbox.

Dropbox has reset passwords for affected users and is rolling out additional protections. But the incident underscores a persistent problem: credential stuffing attacks remain one of the most effective ways for hackers to get in. No fancy exploits needed, just a list of leaked passwords and a bit of patience.

How to Protect Yourself

  • Use a unique password for every account. Yes, every single one.
  • Enable two-factor authentication, especially on cloud storage and email.
  • Check haveibeenpwned.com to see if your credentials have been exposed.
  • If you’re a Dropbox user, change your password now, even if you weren’t affected.

It’s tedious, but it works. The hackers who did this weren’t geniuses — they were just counting on people to make the same mistake twice.

Guardio Hits $1.1 Billion Valuation

In brighter news, Guardio, a browser security startup, has reached a valuation of $1.1 billion. The company, which focuses on protecting consumers from phishing, malware, and malicious extensions, has been growing quietly but steadily.

Guardio’s approach is simple: a lightweight browser extension that blocks threats before they reach the user. It’s a consumer-focused product, but the underlying tech has broader implications. As more people work from home, the browser has become the new perimeter.

The Guardio funding round signals that investors see value in endpoint protection that doesn’t require a degree in cybersecurity to operate. That’s a good sign for the industry, and an even better one for users who just want to browse without getting hacked.

Why These Stories Matter

On the surface, these three items seem disconnected. A cloud patch, a credential stuffing attack, and a funding round — what’s the thread?

It’s this: security is a moving target. Microsoft’s patches show that even the giants are constantly fixing holes. The Dropbox incident shows that human behavior — password reuse, ignored 2FA — often undoes even the best technical defenses. And Guardio’s valuation shows that the market rewards products that make security accessible.

None of these stories will dominate tomorrow’s headlines. But together, they paint a picture of an industry that’s always fighting, always adapting, and always finding new ways to protect users. That’s worth paying attention to, even if it doesn’t make the front page.

Stay patched, stay vigilant, and for heaven’s sake, stop reusing your passwords.

Continue Reading

Trending